VulnTracker Blog
  • Home
  • About

Kaan Koç

CVE-2026-41709: VMware ESX Logging Flaw Added to CISA KEV After Warp Panda Used It to Hide Activity

VMware

CVE-2026-41709: VMware ESX Logging Flaw Added to CISA KEV After Warp Panda Used It to Hide Activity

A VMware ESX logging flaw scored 2.7 out of 10 is now on CISA KEV. CrowdStrike says the China-nexus group Warp Panda used it as a zero-day to perform admin operations without being logged. Here is who is affected, the fixed builds, and what to do.
By Kaan Koç 29 Oct 2026
CVE-2026-46300: Linux Kernel Flaw Added to CISA KEV After PHP2Shell Attacks Chained It for Root

CISA KEV

CVE-2026-46300: Linux Kernel Flaw Added to CISA KEV After PHP2Shell Attacks Chained It for Root

CISA added the Linux kernel flaw Fragnesia to KEV on Oct 28. A 7.8 on its own, it was chained with PHP2Shell to root 25 servers. Fixed kernels and what to check.

By Kaan Koç 29 Oct 2026
Adobe Commerce PolyShell and Google Brotli: Two CVEs Added to CISA KEV on October 27, 2026

CISA KEV

Adobe Commerce PolyShell and Google Brotli: Two CVEs Added to CISA KEV on October 27, 2026

CISA added the Adobe Commerce PolyShell flaw and a Google Brotli decoder bug to KEV on Oct 27. One was patched in July, the other six days earlier. Affected versions and what to check.

By Kaan Koç 28 Oct 2026
CVE-2026-109618 and CVE-2026-109619: CISA Adds PHP2Shell to KEV After Confirmed Attacks

CISA KEV

CVE-2026-109618 and CVE-2026-109619: CISA Adds PHP2Shell to KEV After Confirmed Attacks

CISA added both PHP2Shell flaws to KEV on Oct 26. Exploitation is confirmed on a honeypot and exploit code is public. Fixed PHP versions, affected products and what to check.

By Kaan Koç 27 Oct 2026
Exploited CVEs Oct 19-25, 2026: Plex, Arista, Collabora, Siemens and SiteGuard

Weekly Digest

Exploited CVEs Oct 19-25, 2026: Plex, Arista, Collabora, Siemens and SiteGuard

Eight CVEs from five vendors joined CISA KEV this week, with scores from 4.3 to 9.9. Plex2Shell, Siemens ClickFix, SiteGuard, Arista and Collabora, plus where PHP2Shell fits.

By Kaan Koç 26 Oct 2026
Arista VeloCloud and Collabora Online: Two CVEs Added to CISA KEV on October 23, 2026

CISA KEV

Arista VeloCloud and Collabora Online: Two CVEs Added to CISA KEV on October 23, 2026

Two critical flaws joined CISA KEV on Oct 23, both due Oct 26. One turns any VeloCloud Orchestrator user into a superuser operator. The other allows unauthenticated command execution on Nextcloud servers.

By Kaan Koç 24 Oct 2026
CVE-2026-115560: PHP Warns of Another Unpatched RCE Path Days After PHP2Shell

PHP2Shell

CVE-2026-115560: PHP Warns of Another Unpatched RCE Path Days After PHP2Shell

Two days after the PHP2Shell emergency fixes, PHP warned of CVE-2026-115560, an unlikely RCE vector in session upload progress. There is no patch yet, only a one-line setting. Here is what PHP has said, what it has not, and how to keep it apart from the attacks already under way.

By Kaan Koç 23 Oct 2026
CVE-2026-110264: GitLab Critical RCE Reaches Back to Version 7.0

GitLab

CVE-2026-110264: GitLab Critical RCE Reaches Back to Version 7.0

GitLab fixed a CVSS 10 flaw that could let an unauthenticated attacker run code on self-managed servers, in a release that closes 12 vulnerabilities. Here are the fixed versions, what GitLab has not said, and what to do now.

By Kaan Koç 22 Oct 2026
PHP Ships Emergency Fixes for CVE-2026-109618 and CVE-2026-109619

PHP2Shell

PHP Ships Emergency Fixes for CVE-2026-109618 and CVE-2026-109619

PHP shipped 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on October 21 to fix two critical remote code execution flaws. The advisories confirm what the warning left open: which setups are at risk, how the bugs work, and what to do if you cannot update today.

By Kaan Koç 21 Oct 2026
PHP2Shell: Two Critical PHP RCE Flaws, CVE-2026-109618 and CVE-2026-109619

PHP2Shell

PHP2Shell: Two Critical PHP RCE Flaws, CVE-2026-109618 and CVE-2026-109619

PHP warned of two critical remote code execution flaws, both rated CVSS 4.0 9.2, ahead of an emergency release on October 21. Here is what is confirmed, what is not, and how to prepare before the details are published.

By Kaan Koç 21 Oct 2026
Exploited CVEs Last Week: October 12-18, 2026

Weekly Digest

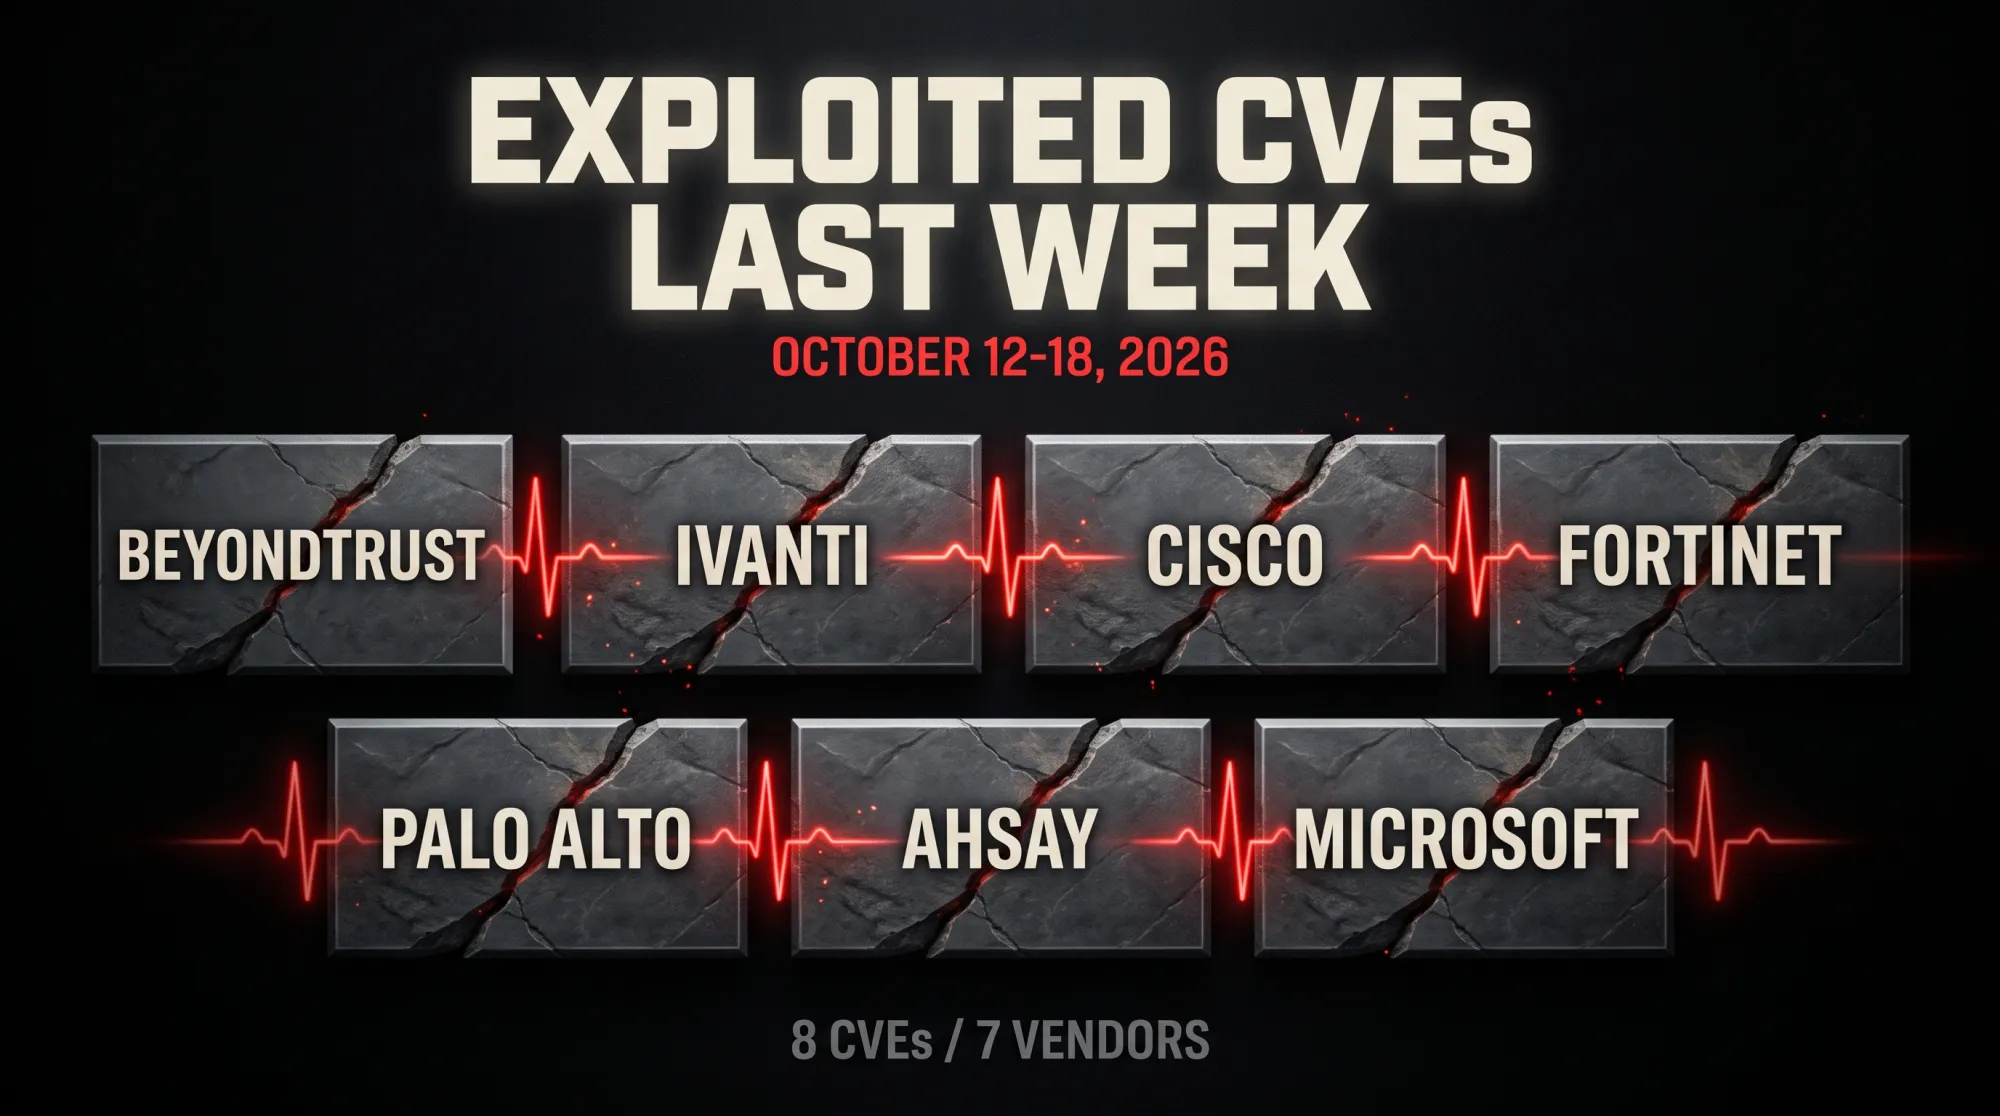
Exploited CVEs Last Week: October 12-18, 2026

Eight exploited CVEs from seven vendors entered CISA's KEV catalog between October 13 and 16. Five sit on edge or remote access products, seven had an EPSS of 5% or less, and all are marked Active in SSVC. Here is the list, the angle and what to patch first.

By Kaan Koç 19 Oct 2026
CVE-2026-102764: BeyondTrust Remote Support Zero-Day Used in China-Linked Intrusions

Zero-Day

CVE-2026-102764: BeyondTrust Remote Support Zero-Day Used in China-Linked Intrusions

BeyondTrust patched a critical Remote Support flaw on October 15, but a China-linked group had been exploiting it since August 29. Here is what the attackers did, who must patch, and how to check an appliance for compromise.

By Kaan Koç 17 Oct 2026
See all
VulnTracker Blog
  • Sign up
Powered by Ghost