VulnTracker Blog
  • Home
  • About

Kaan Koç

CVE-2026-123039: Check Point Gaia OS Root Escalation Exploited in Gateway Attacks, Added to CISA KEV

CISA KEV

CVE-2026-123039: Check Point Gaia OS Root Escalation Exploited in Gateway Attacks, Added to CISA KEV

CISA added a Check Point Gaia OS root escalation to KEV on November 13, 2026, due November 16. Check Point saw it used against a couple of dozen customers. Reports describe it as step two after a webshell lands. This post lists the fixed Jumbo Hotfix takes and what to check.
By Kaan Koç 14 Nov 2026
CVE-2026-124194: Outlook Spoofing Flaw Exploited as a Zero-Day, Added to CISA KEV

CISA KEV

CVE-2026-124194: Outlook Spoofing Flaw Exploited as a Zero-Day, Added to CISA KEV

Microsoft fixed an exploited Outlook flaw on November 10, 2026. Opening a crafted message file can make Outlook skip its external-content warning and leak an NTLMv2 hash. CISA added it to KEV the same day, due November 24. This post lists fixed builds and what to check.

By Kaan Koç 13 Nov 2026
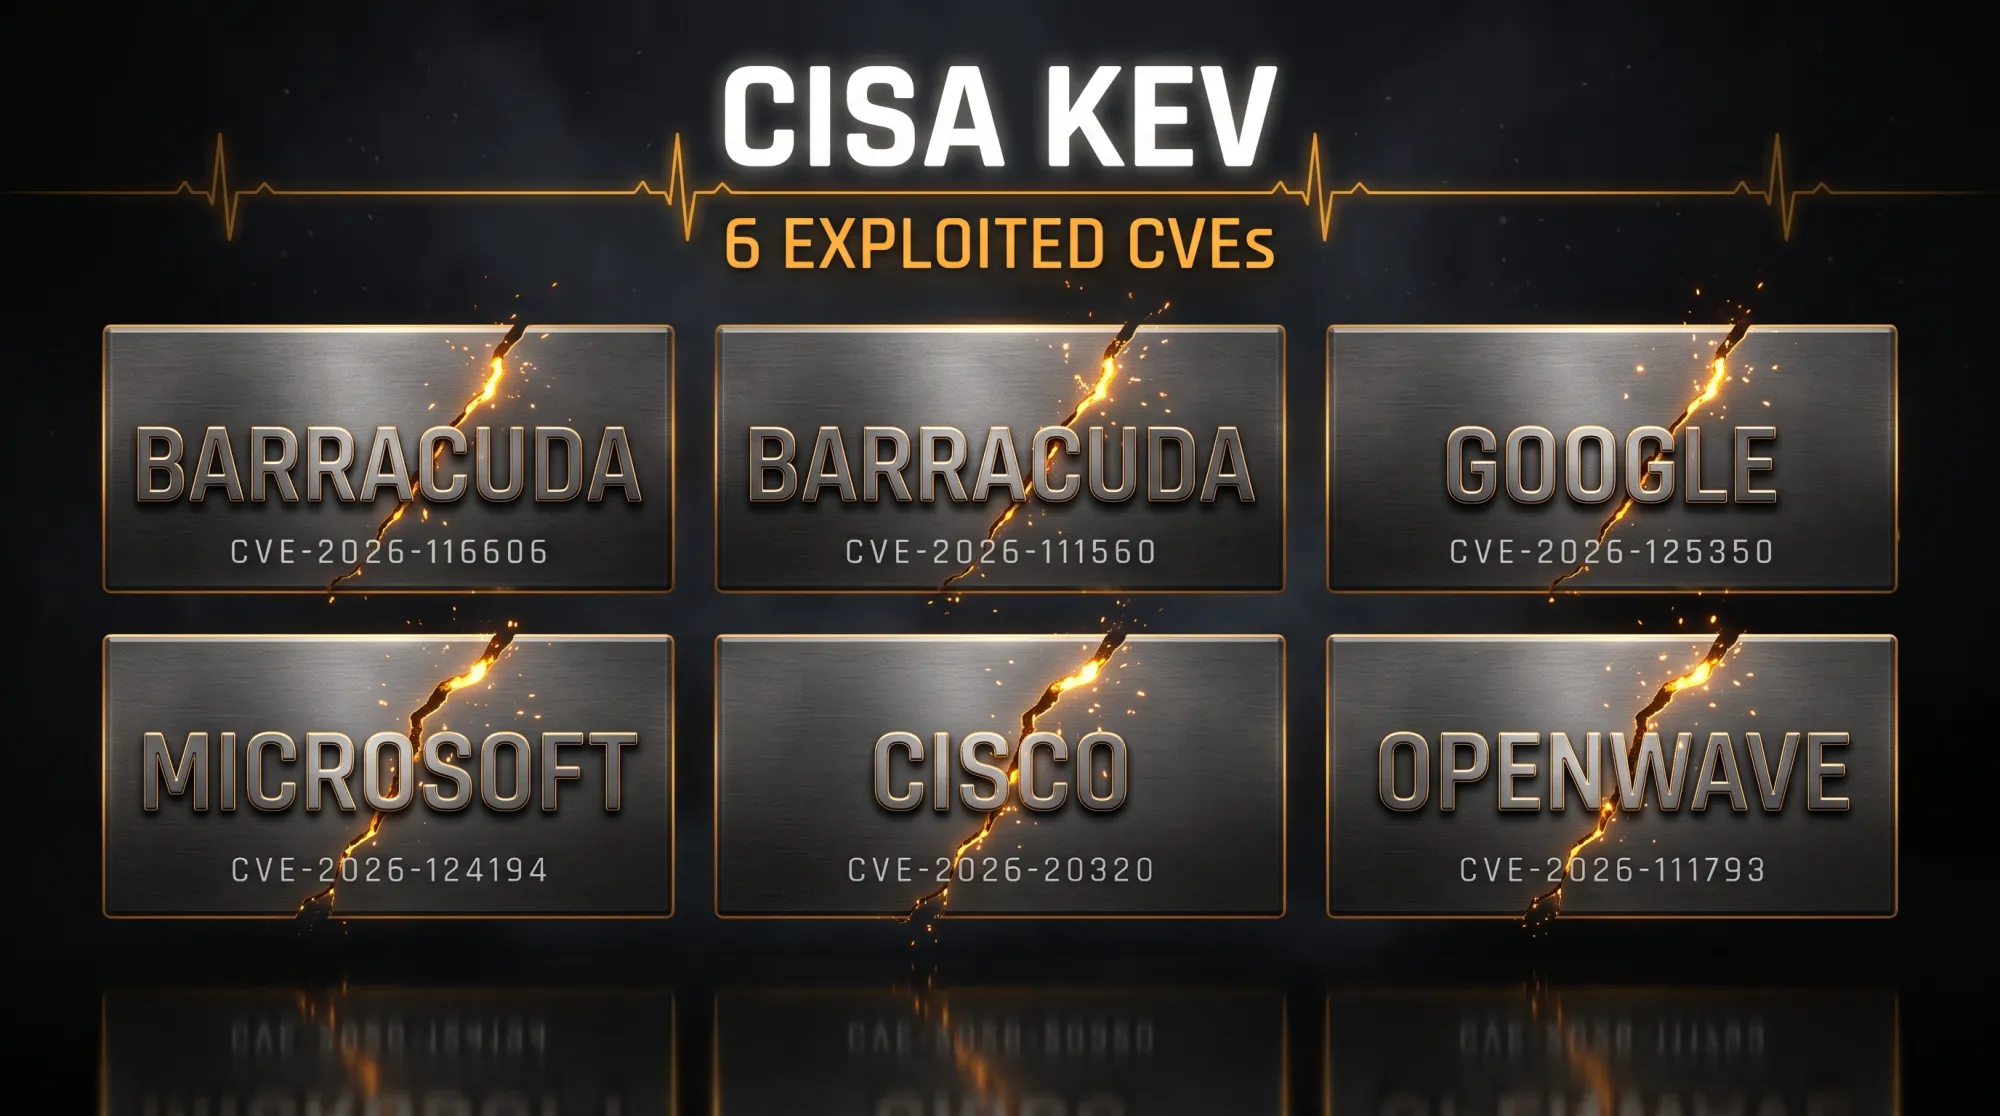
Six Exploited CVEs Added to CISA KEV on Nov 10: Barracuda, Chrome, Outlook, Cisco BroadWorks, Openwave

CISA KEV

Six Exploited CVEs Added to CISA KEV on Nov 10: Barracuda, Chrome, Outlook, Cisco BroadWorks, Openwave

CISA added six actively exploited flaws to KEV on November 10, 2026. Two Barracuda flaws are due November 13 and four more are due November 24: Chrome, Outlook, Cisco BroadWorks and Openwave. Every fix was public by listing day, from 83 days earlier to the same day.

By Kaan Koç 11 Nov 2026
OpenSSH, GPUStack, FreeSWITCH and IBM Aspera Faspex: Four Exploited Flaws Added to CISA KEV

CISA KEV

OpenSSH, GPUStack, FreeSWITCH and IBM Aspera Faspex: Four Exploited Flaws Added to CISA KEV

CISA added four actively exploited flaws to KEV on November 9, 2026, all due November 12. Each has a vendor fix. This post covers IBM Aspera Faspex, FreeSWITCH, OpenSSH (SSHole) and GPUStack, what each one needs, and what to check after patching.

By Kaan Koç 10 Nov 2026
Exploited CVEs Nov 2-8, 2026: WordPress, Apple, SonicWall

Weekly Digest

Exploited CVEs Nov 2-8, 2026: WordPress, Apple, SonicWall

Three exploited CVEs entered CISA KEV last week: WordPress Core, Apple WebKit and SonicWall SonicOS. Each had a vendor fix before the listing, from six days to 905 days earlier. Here is the week in one place, with deadlines and what to patch first.

By Kaan Koç 09 Nov 2026
CVE-2026-19868: SonicWall SonicOS SSLVPN SAML Bypass Added to CISA KEV

SonicWall

CVE-2026-19868: SonicWall SonicOS SSLVPN SAML Bypass Added to CISA KEV

CISA put a SonicOS SSLVPN flaw on KEV the day its CVE was published. A valid credential for an alternate login method can bypass SAML and MFA. Here is who is affected, the fixed builds, and what to do.

By Kaan Koç 07 Nov 2026
CVE-2026-83844: Windows Paint RCE With Conflicting Fixed-Version Reports

Microsoft

CVE-2026-83844: Windows Paint RCE With Conflicting Fixed-Version Reports

A Windows Paint out-of-bounds read can lead to code execution over a network. It scores 8.1 and is not known to be exploited, but the reported fixed build differs by source. Here is who is affected and how to update.

By Kaan Koç 06 Nov 2026
CVE-2024-27834: Patched Apple WebKit Flaw Added to CISA KEV as Part of an Exploit Chain

CISA KEV

CVE-2024-27834: Patched Apple WebKit Flaw Added to CISA KEV as Part of an Exploit Chain

CISA put an Apple WebKit flaw patched in May 2024 on KEV. It scores 5.5, yet Sekoia ties it to an exploit chain that ends in cookie theft. Here is who is affected, the fixed versions, and what to do.

By Kaan Koç 05 Nov 2026
CVE-2026-119977: WordPress Core Upgrade-Window Flaw Added to CISA KEV After Attacks on the Staged Installer

CISA KEV

CVE-2026-119977: WordPress Core Upgrade-Window Flaw Added to CISA KEV After Attacks on the Staged Installer

A WordPress Core race condition that runs code during a core update is now on CISA KEV. Attackers are polling the staging path and waiting for sites to update. Here is who is affected, the fixed versions, and what to do.

By Kaan Koç 04 Nov 2026
Exploited CVEs Oct 26-Nov 1, 2026

Weekly Digest

Exploited CVEs Oct 26-Nov 1, 2026

Nine CVEs from eight vendors joined CISA KEV last week, from a 2.7 VMware logging flaw to a CVSS 10.0 GitLab bug. Same SSVC tags got three-day and 14-day deadlines, so here is what to patch first and why.

By Kaan Koç 02 Nov 2026
CVE-2026-111357: Ivanti Connect Secure Root Escalation Added to KEV as the Last Link in a Zero-Day Chain

Ivanti

CVE-2026-111357: Ivanti Connect Secure Root Escalation Added to KEV as the Last Link in a Zero-Day Chain

A 7.0 rated Ivanti Connect Secure flaw is now on CISA KEV. It was the last step of a three-exploit chain that reached root on a fully patched appliance. Here are the fixed builds and why a clean integrity check is not enough.

By Kaan Koç 31 Oct 2026
CVE-2026-76418 and CVE-2026-97229: Cisco ASA/FTD and GitLab Flaws Hit KEV With a Three-Day Deadline

Cisco

CVE-2026-76418 and CVE-2026-97229: Cisco ASA/FTD and GitLab Flaws Hit KEV With a Three-Day Deadline

CISA added a Cisco firewall VPN flaw and a CVSS 10.0 GitLab RCE to KEV on the same day, both due November 1. Here are the affected versions, the fixes, and why checking the version alone can leave you exposed.

By Kaan Koç 30 Oct 2026
See all
VulnTracker Blog
  • Sign up
Powered by Ghost